
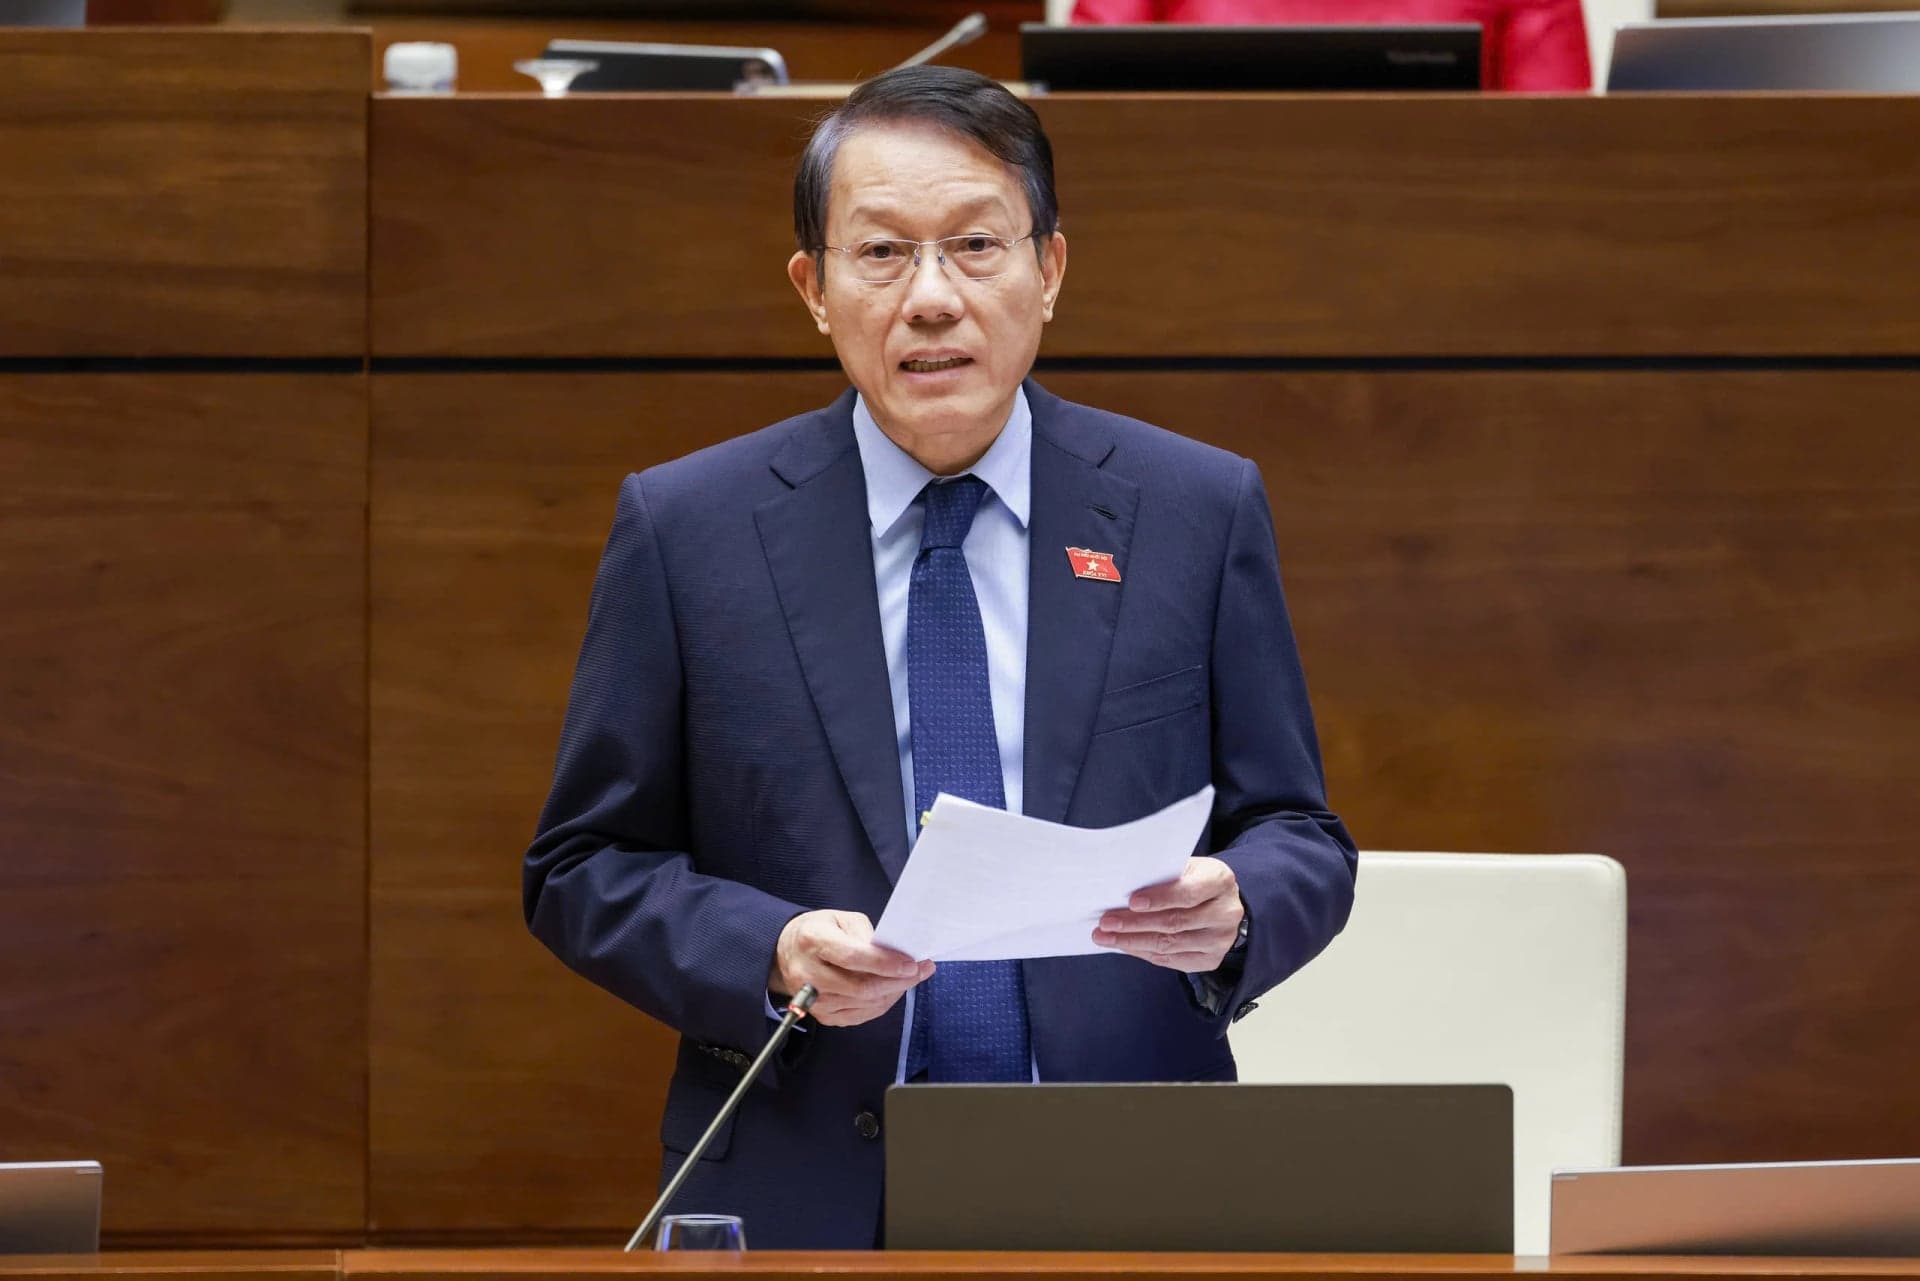
Vietnamese Minister of Public Security Luong Tam Quang explained the draft laws on electronic identification and authentication and on data security to lawmakers at the end of a discussion during the second session of the 16th National Assembly on the morning of November 4.
The minister said that only a proper assessment of the harm data could cause if compromised would allow lawmakers to set proportionate obligations. This would avoid broad protection in low-risk areas while leaving high-risk areas exposed.
Electronic identification and privacy protection
Article 7 of the draft law on electronic identification defines the groups that can receive an electronic identity. Article 8 separately lists groups identified by state agencies, including agencies and organizations, individuals, national locations and high-risk goods, among other categories.
Under the draft, agencies, organizations and individuals would not have to provide their information again to create an electronic identity or register for electronic identification.
Luong Tam Quang also said the draft sets out several layers of privacy protection: collecting only the minimum necessary data with the data subject's consent, not synchronizing transaction content, and not sharing authentication results beyond the permitted scope.
"Personal data protection in electronic identification and authentication is carried out strictly in accordance with personal data protection legislation," the minister said. He added that the use of electronic identities must keep information confidential and comply with the law.
The minister said the drafting body would continue reviewing related provisions and advise the government on detailed rules for collecting, accessing and using electronic identification and authentication data. He said this would provide strict protection for the lawful rights and interests of data subjects.
The draft also says that agencies, organizations and individuals using electronic transaction accounts for online transactions in securities, telecommunications, banking, postal services, e-commerce, medical care and other fields involving risk or important legal consequences must authenticate with the national electronic identity and link their electronic transaction account to it.
Five data security risk levels
Speaking about the draft data security law, Luong Tam Quang said that defining data security risk levels and a mechanism for assigning them was a foundation of the bill. "Only a proper assessment of the harm caused by a data breach makes it possible to set proportionate obligations, so that low-risk areas are not overprotected while high-risk areas are not left exposed," the minister said.
Following conclusions from the National Assembly Standing Committee, the draft sets out five risk levels corresponding to the five information-system levels under the Cybersecurity Law. The lower the risk, the simpler the procedure.
Level-one data would require no procedure. For level-two data, a shortened protection plan would be enough, with exemptions for household businesses, micro and small enterprises, and innovative start-ups.
Impact assessments and audits would be required from level three. Appraisal would apply only to levels four and five and would be conducted in the same dossier as the cybersecurity appraisal.
The minister proposed retaining an option under which the government would set the risk levels. If fixed in the law, every adjustment would require an amendment. When preparing the decree, the government would set verifiable quantitative and qualitative criteria so businesses, especially small and medium-sized enterprises, could determine the correct level without being assessed above what is necessary.
On the division of responsibility between the Ministry of Public Security and the Ministry of National Defence for state management of data security in the civil and economic activities of businesses, Luong Tam Quang said this was not a new provision but an institutionalization of Directive 57 of the Party Central Committee Secretariat.
Under the draft, the Ministry of Public Security would be accountable to the government and lead state management of cybersecurity, information security and data security. The Ministry of National Defence would lead the management of information systems, military databases and cryptographic systems within the defence sector. The minister said this arrangement follows the principle that one agency leads and bears primary responsibility for one task, complies with Resolution 18 and is consistent with the model approved by the National Assembly in the 2025 Cybersecurity Law.
Sources: Thanh Niên

